Why Image Security Deserves a Layered Approach
Pictures now carry much of the information exchanged online, and that includes material of a personal, medical, or otherwise sensitive nature. When such imagery falls into the wrong hands, the consequences range from identity fraud and fabricated claims to a broader loss of confidence in digital systems.
No single mechanism closes all of these gaps. A practical strategy combines four elements: provenance marking that is imperceptible to viewers, defenses that harden vision models against crafted inputs, face de-identification that reduces exposure while keeping data usable, and cryptographic protection for images in storage and transit. The sections below define each element, describe representative techniques, and note where trade-offs arise.
Imperceptible Provenance Marking for Synthetic Imagery
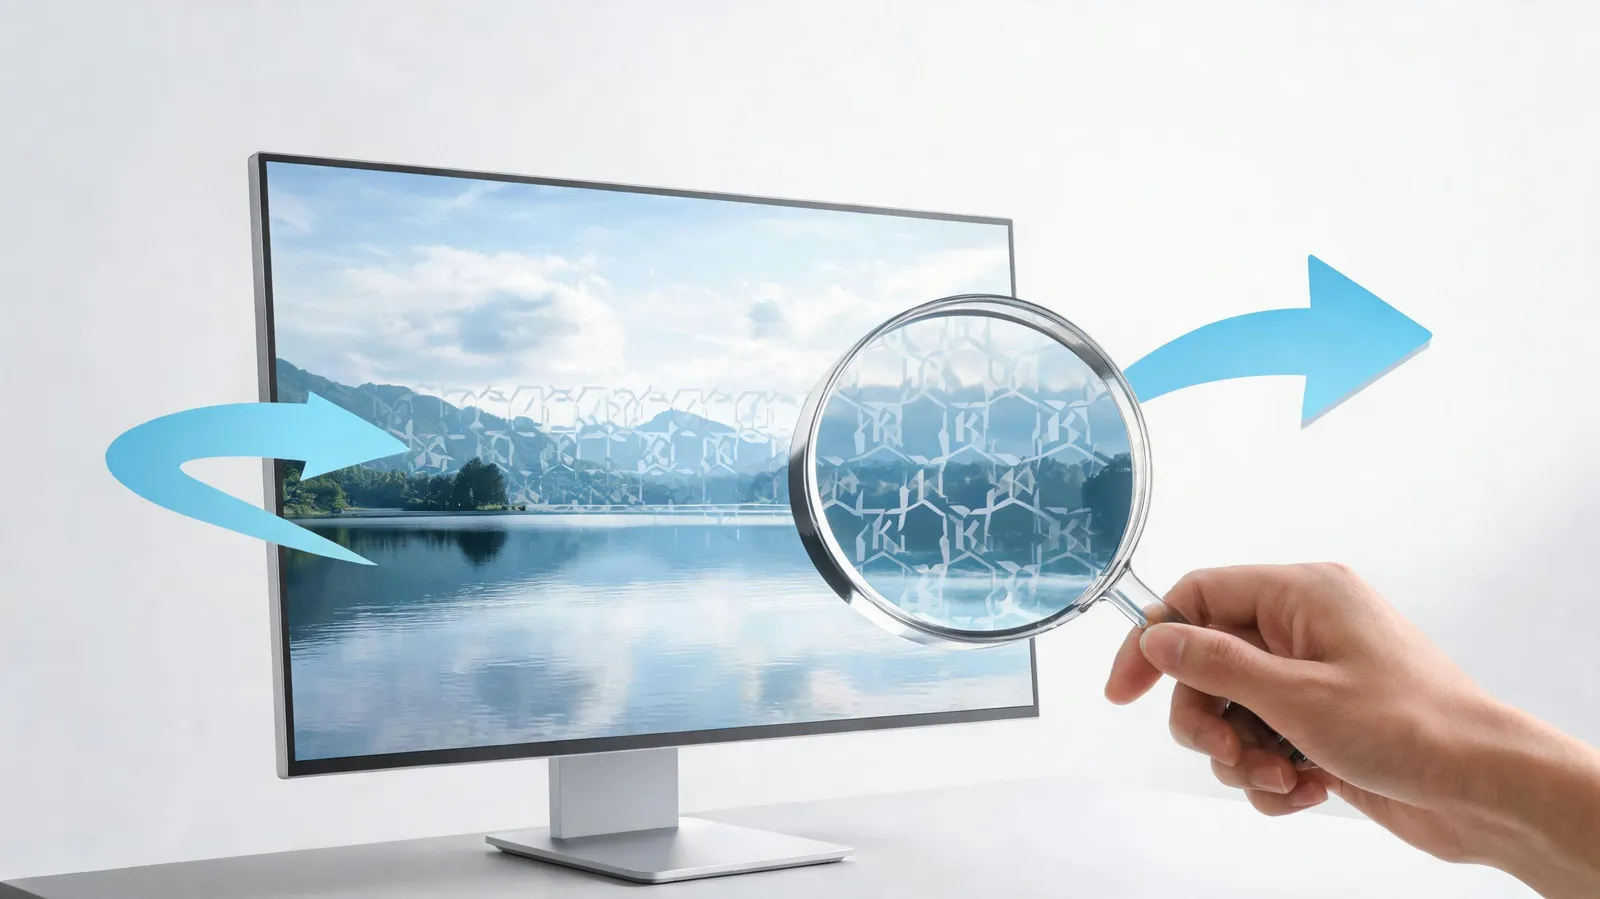
Embedding ownership or origin details into a picture so that the human eye cannot detect the change is what distinguishes provenance marking from conventional visible logos. The mark is recoverable by algorithmic detection, which makes it useful for confirming whether content was machine-generated, for tracing copyright, and for countering manipulated media.
It is worth separating this from related practices. Steganography conceals secret messages, and metadata tags are easily stripped; provenance marking instead prioritizes durability and invisibility. Typical applications include rights protection, authenticity checks, and indicating synthetic origin—several AI generators, among them OpenAI, already embed such marks.
Method families differ in where they operate. Spatial approaches alter pixel values directly, whereas frequency-domain methods such as DCT and DWT place marks in transformed coefficients. Learning-based schemes rely on GANs or diffusion models to embed signals that resist tampering. Findings from recent studies indicate that learning-based marks can persist through compression, cropping, and added noise.
Performance is commonly assessed with PSNR, SSIM, and BER. There is a recurring tension: stronger resistance to removal tends to make the mark more noticeable. Since attackers may compress, crop, or adversarially strip a watermark, practical deployment depends on striking the right balance for the intended use.
Crafted Perturbations Against Vision Models, and How to Counter Them
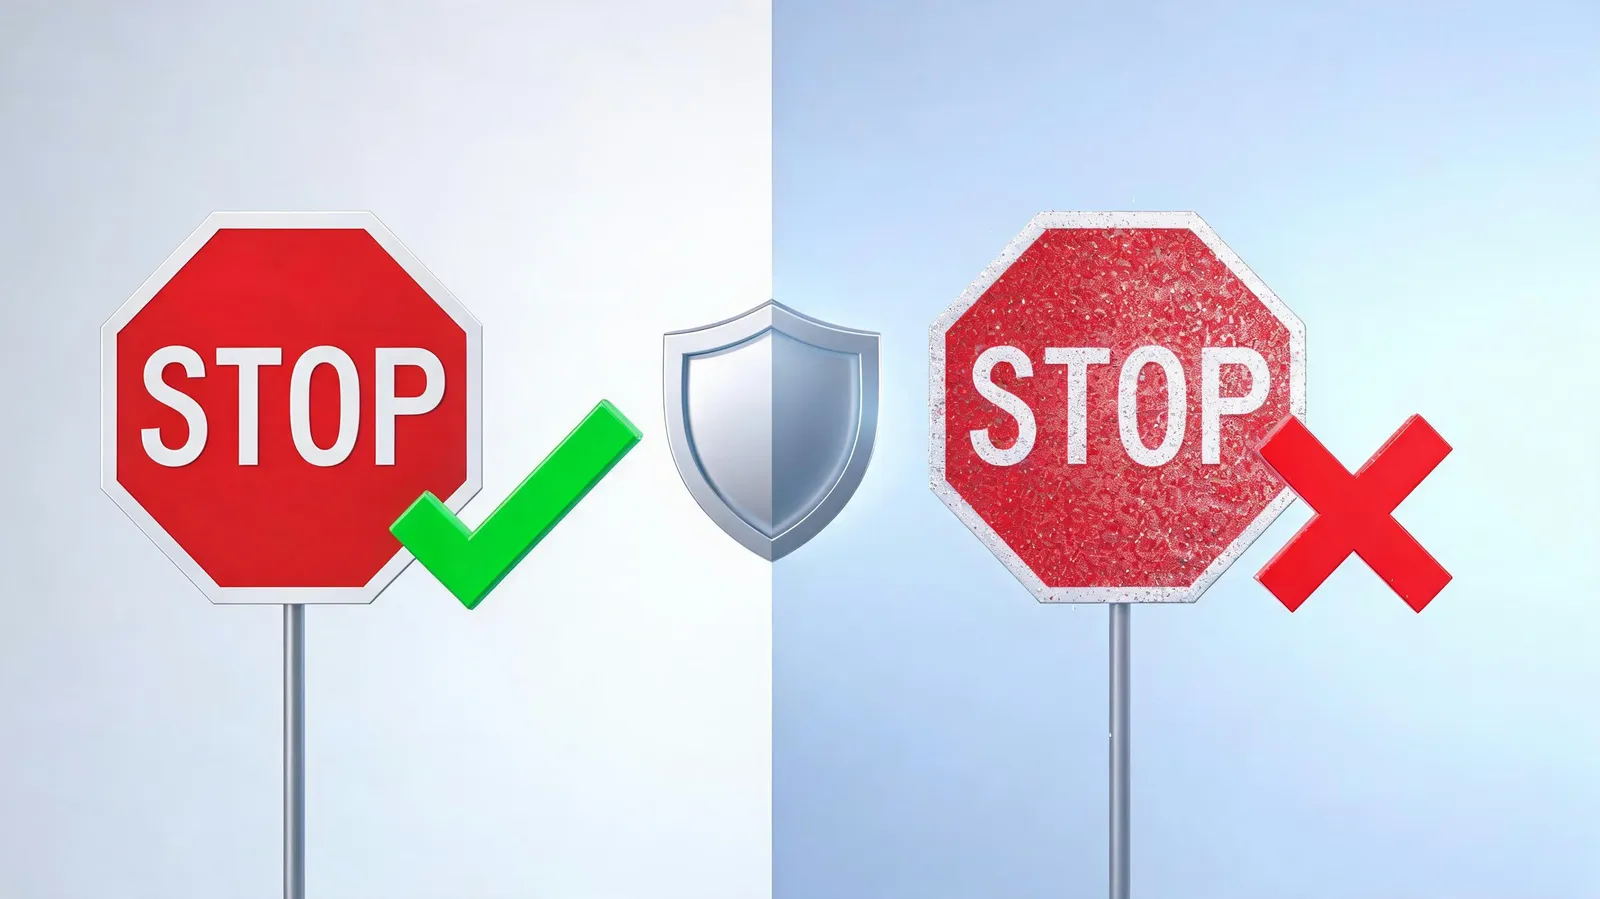
Adding small, frequently undetectable changes to an image can cause a vision model to output the wrong label. Such attacks matter in driving automation, medical analysis, and security screening—a stop sign carrying subtle noise, for instance, might be read as a speed-limit sign with dangerous results.
Common attack strategies include FGSM, PGD, and patch-based methods, all of which exploit weaknesses in model behavior and can cause misclassification in high-stakes settings. On the defensive side, options include adversarial training, input preprocessing, and certified approaches such as randomized smoothing; each brings a cost, since hardening a model often reduces its accuracy.
Watermarks are not immune. Adversarial methods can be used to erase or counterfeit provenance marks, so a robust marking scheme has to anticipate this and pair with stronger countermeasures. Current work in this area concentrates on detecting and removing the crafted perturbations themselves.
Face Recognition, Privacy Exposure, and De-Identification
Mass surveillance, persistent tracking, and misuse of collected data have made facial recognition a focal point of privacy debate. Legal instruments such as GDPR and BIPA are intended to shield individuals, though enforcement remains difficult. De-identification offers a way to keep some utility while limiting exposure.
Unauthorized deployments can follow people without their agreement, and documented cases underscore why strict rules and ethical practice matter. Familiar de-identification options include blurring, masking, adversarial perturbation, and generation of synthetic faces. To be useful, these techniques need to defeat current recognition models without destroying the image's purpose.
Differential privacy applied to face embeddings, together with federated learning, provides privacy-preserving alternatives. In security and healthcare contexts, the de-identification method must not break the underlying task; adding noise to embeddings and keeping data decentralized are two ways to pursue that balance.
Protecting Stored and Transmitted Images
Images are exposed both at rest and while moving between systems, with breaches, unauthorized entry, and tampering among the main threats. Weaknesses in cloud storage make end-to-end encryption a practical necessity.
Encryption options include AES, homomorphic encryption, and secure multi-party computation, and their performance with large image collections is a real consideration. Medical imaging and cloud photo libraries are common use cases.
Decentralized architectures add another layer. IPFS and blockchain-anchored watermarking can support integrity and origin verification, while smart contracts can govern who is allowed access. Together these provide storage that is resistant to tampering and easier to audit.
Bringing the Layers Together
Imperceptible marking, hardened models, face de-identification, and protected storage are complementary rather than interchangeable. Combining them with newer developments—federated learning, encryption designed to resist quantum attack, and evolving regulation—will matter as AI systems grow more capable. Adopting this layered posture is one way to keep trust, privacy, and integrity intact in visual systems driven by AI.