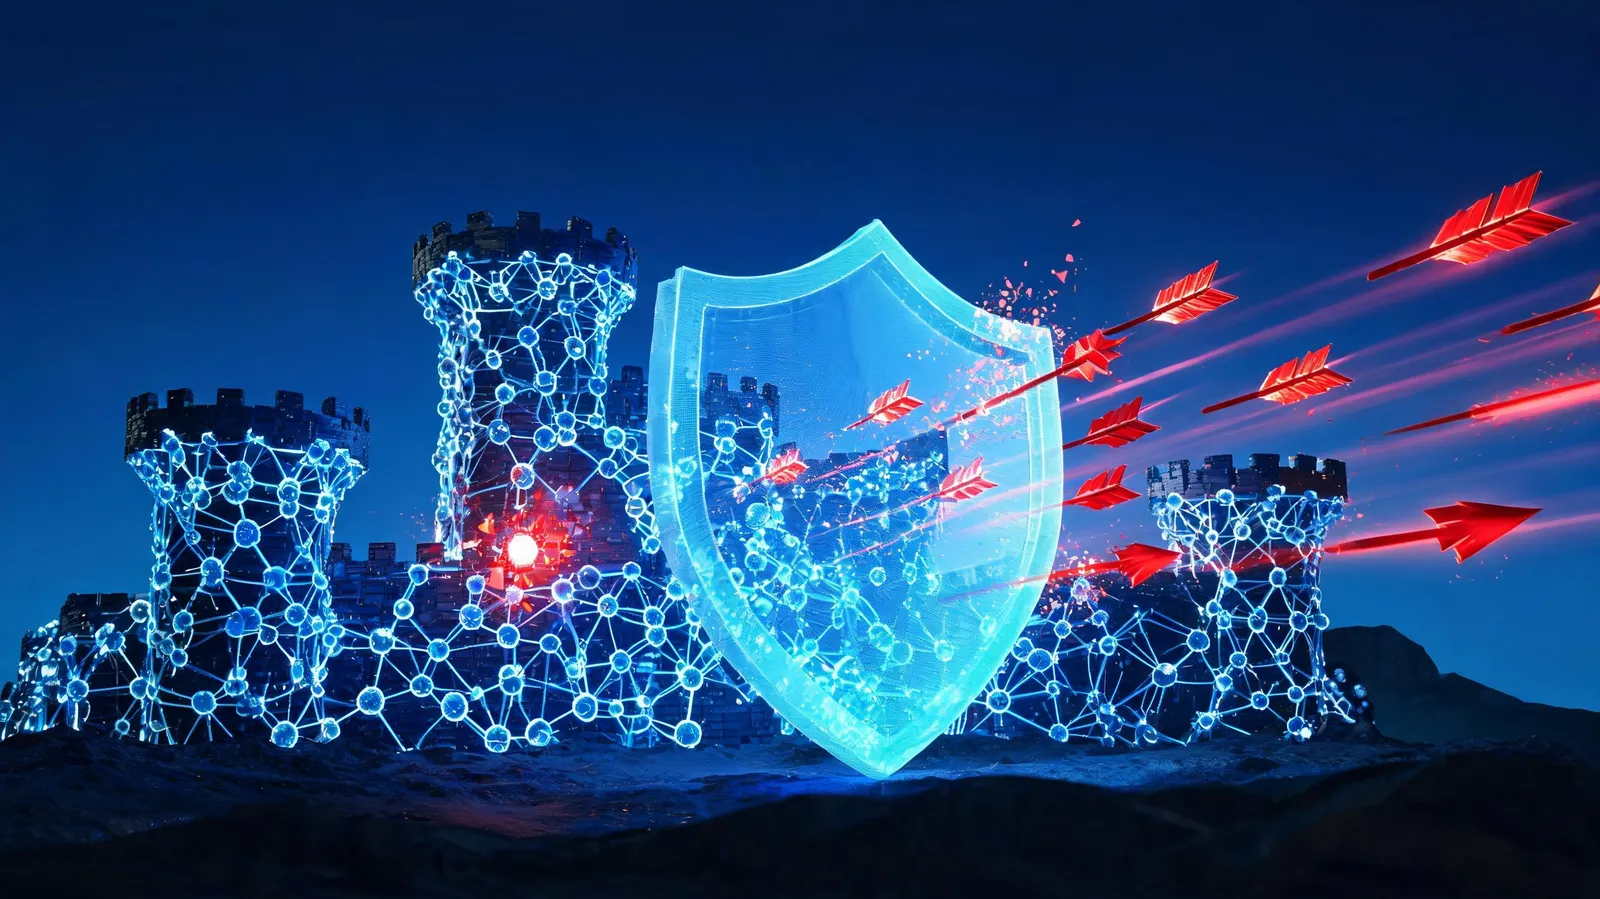
As AI systems gain autonomy and find their way into critical infrastructure, debugging them is no longer just about eliminating software errors. It now requires defending against sophisticated adversarial threats, ensuring regulatory compliance, and maintaining public trust. This article explores the essential pillars of secure AI debugging: adversarial robustness, auditability, incident response, and regulatory alignment, providing a comprehensive framework for building resilient AI systems.
Debugging Adversarial Attacks and Model Vulnerabilities
Adversarial attacks are among the most insidious threats to AI systems. They exploit model weaknesses by introducing carefully crafted inputs designed to cause misclassification, evasion, or data leakage. Common vectors include data poisoning, where attackers corrupt training data; evasion attacks, which manipulate inputs at inference time; and model inversion, which extracts sensitive training data. A notable case is the 2023 attack on a facial recognition system used in a major U.S. airport, where researchers demonstrated that subtle perturbations to images could bypass security checks. According to a 2024 study by the AI Security Institute, over 70% of deployed machine learning models exhibit at least one high-severity adversarial vulnerability.
Debugging for adversarial robustness requires a multi-layered approach. Adversarial training, where models are trained on adversarial examples, improves resilience. Input sanitization filters malicious perturbations before inference. Anomaly detection monitors for unusual patterns that may indicate an attack. Tools like IBM's Adversarial Robustness Toolbox (ART) and Google's CleverHans provide frameworks for testing and hardening models. A comparison of defense strategies shows that while no single method is foolproof, combining adversarial training with input validation reduces successful attack rates by up to 85%.
When debugging, engineers should conduct regular red-team exercises to simulate attacks and identify weaknesses. Automated tools can scan for known vulnerabilities, but human expertise remains crucial for interpreting results and devising mitigations. By integrating security into the debugging lifecycle, organizations can build AI that withstands adversarial pressure.
Auditability and Traceability Requirements for AI Systems
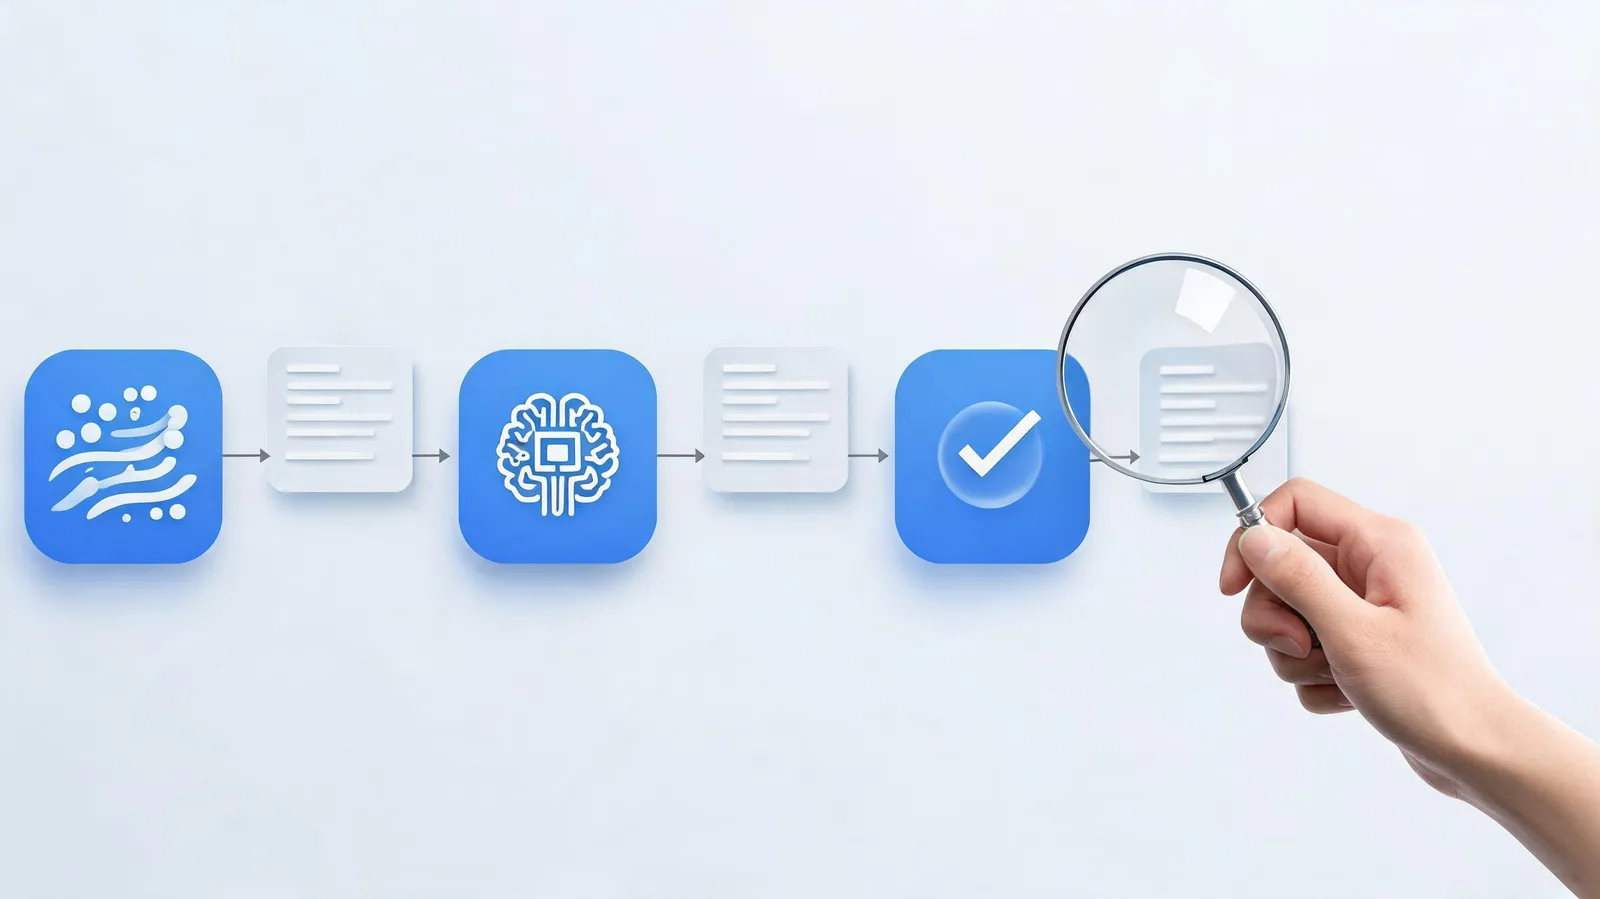
Auditability is the cornerstone of trustworthy AI. It ensures that every decision made by an AI system can be traced, understood, and, if necessary, contested. Regulatory frameworks such as the EU AI Act and GDPR's right to explanation mandate that high-risk AI systems provide transparent reasoning for their outputs. In the U.S., the FTC has begun enforcing similar standards, penalizing companies that deploy opaque AI in sensitive domains like hiring or lending.
Implementing auditability requires robust logging and traceability mechanisms. At each stage of the AI pipeline—data ingestion, preprocessing, model inference, and output—audit logs should capture inputs, outputs, model versions, and decision rationales. Best practices for audit log design include using immutable storage, timestamping, and cryptographic hashing to prevent tampering. Tools like MLflow and Weights & Biases offer experiment tracking, while specialized solutions like Fiddler AI provide model explainability and monitoring.
Transparent and explainable AI (XAI) techniques, such as LIME and SHAP, help demystify black-box models by attributing predictions to input features. For debugging, this means engineers can pinpoint why a model failed and correct it. For compliance, it provides evidence of due diligence. A well-designed audit trail not only aids debugging but also serves as a legal record, reducing liability in case of incidents.
Incident Response and Postmortems for AI Failures
Even the most robust AI systems can fail. When they do, a swift and structured incident response is critical. The NIST Incident Response Framework, adapted for AI, outlines four phases: detection, containment, eradication, and recovery. Detection involves monitoring for anomalies, such as sudden drops in accuracy or unexpected outputs. Containment isolates the affected system to prevent cascading failures. Eradication removes the root cause, whether it's a software bug, a poisoned model, or a data drift issue. Recovery restores the system to normal operation, often with enhanced safeguards.
A case in point is the 2022 incident where a recommendation AI for a major e-commerce platform began promoting harmful content. The company's incident response team quickly detected the anomaly, rolled back the model to a previous version, and conducted a thorough investigation. The postmortem revealed that a subtle change in user behavior had triggered the model to exploit a latent bias. By sharing lessons learned, the team improved data validation and added bias detection, preventing recurrence.
Blameless postmortems are essential for learning from failures. They focus on systemic issues rather than individual blame, encouraging transparency. Steps include gathering timeline data, identifying contributing factors, and proposing actionable improvements. For AI debugging, postmortems should also examine model interpretability, data quality, and deployment processes. By institutionalizing postmortems, organizations foster a culture of continuous improvement and resilience.
Regulatory Compliance and Safety Cases for AI Debugging
The regulatory landscape for AI is rapidly evolving. The EU AI Act categorizes AI systems by risk and imposes strict requirements for high-risk applications, including conformity assessments and post-market monitoring. In the U.S., sector-specific guidelines from the FDA for AI/ML in healthcare and the FTC's enforcement actions set de facto standards. Non-compliance can result in hefty fines—up to 6% of global turnover under the EU AI Act—and reputational damage.
Debugging practices must align with these regulations. This means documenting every step of the development and debugging process to demonstrate compliance. Safety cases, borrowed from industries like aviation and nuclear power, provide a structured argument that an AI system is safe for its intended use. A safety case for AI typically includes a description of the system, its operating environment, identified hazards, risk mitigation measures, and evidence of their effectiveness. Tools like the Assurance of Machine Learning for use in Autonomous Systems (AMLAS) framework help structure such arguments.
For debugging, compliance requirements translate into specific actions: maintaining version control for models and data, conducting regular audits, and ensuring explainability. Automated compliance checks can be integrated into CI/CD pipelines, flagging potential violations early. By treating compliance as a first-class concern, organizations not only avoid penalties but also build trust with users and regulators.
Conclusion
Securing AI systems through debugging is a multifaceted challenge that demands attention to adversarial robustness, auditability, incident response, and regulatory compliance. These pillars are not independent; they reinforce each other. Adversarial debugging ensures models are resilient, auditability provides the transparency needed for trust, incident response minimizes damage when failures occur, and compliance ensures alignment with societal values. Together, they form the foundation of trustworthy AI.
As AI continues to evolve, so will the threats and regulations. Emerging technologies like automated compliance checks and AI-driven security tools promise to ease the burden, but the core principles remain: vigilance, transparency, and accountability. By embedding these into the debugging lifecycle, we can build AI that is not only powerful but also safe, secure, and worthy of trust.