Introduction
Well-executed code review processes can intercept as much as 60% of defects before they reach production. However, tools that are poorly designed can introduce slowdowns and friction for teams. With distributed teams and increasingly complex codebases becoming standard, efficient review workflows have shifted from optional to essential. This article assesses code review and collaboration tools along four critical dimensions: inline comment quality, asynchronous collaboration, version control and issue tracker integration, and automation of review assignment and policy enforcement.
1. Inline Comment Quality and Review Workflows
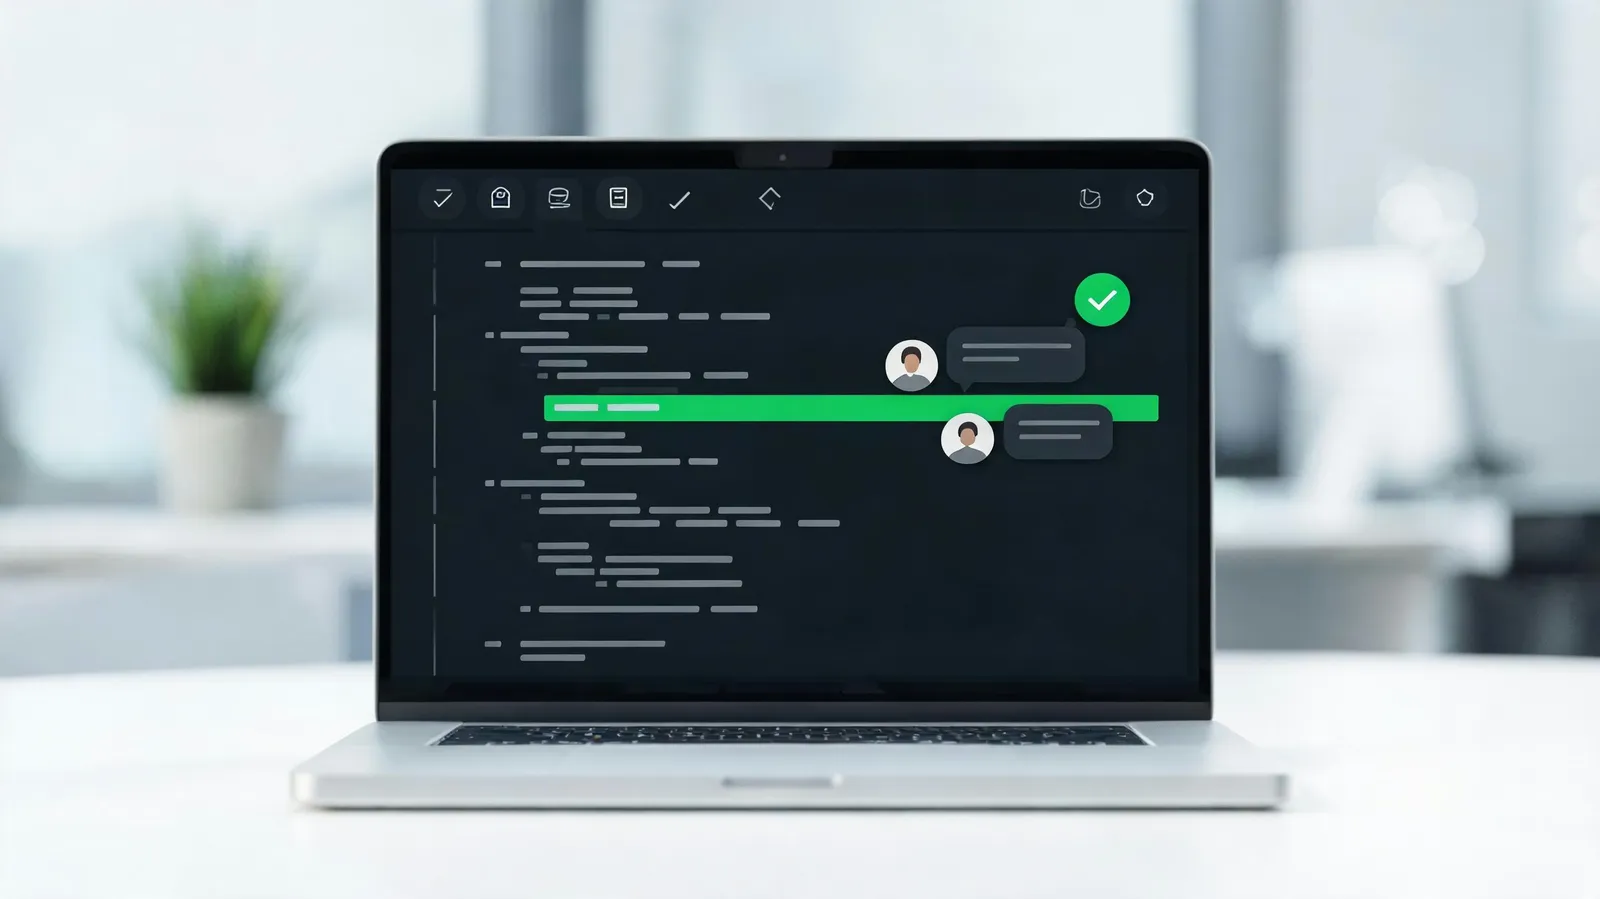
Inline comments form the core of any code review tool, enabling reviewers to pose questions, propose improvements, and discuss specific lines of code directly within the review interface. Features that define high-quality inline comments include threading, @mentions, and the ability to suggest concrete code changes that authors can apply with a single click. GitHub, GitLab, and Phabricator each provide robust inline comment capabilities, though they vary in threading depth, notification granularity, and integration with code suggestions. GitHub's suggestion feature, for instance, allows reviewers to propose exact code replacements, which cuts down on back-and-forth. GitLab supports threaded discussions that can be resolved individually, while Phabricator focuses on large diffs and custom workflows for inline comments. The effect on review turnaround time and defect detection is substantial: teams that use threaded inline comments with suggestions report faster resolution and fewer missed issues.
Equally important is workflow customization. Approval rules, review stages, and required reviewers help ensure that the appropriate people examine the code before it merges. A case study involving a mid-sized US software team found that implementing a two-stage review process with required reviewers for critical modules reduced review cycle time by 30% and decreased post-merge defects by 25%. Built-in workflows are simpler to set up, whereas plugin-based workflows provide more flexibility. Tools such as Reviewable and Gerrit offer advanced workflow customization but may demand more configuration. The key is to align the workflow with the team's size, risk tolerance, and release cadence.
2. Asynchronous Collaboration Across Time Zones
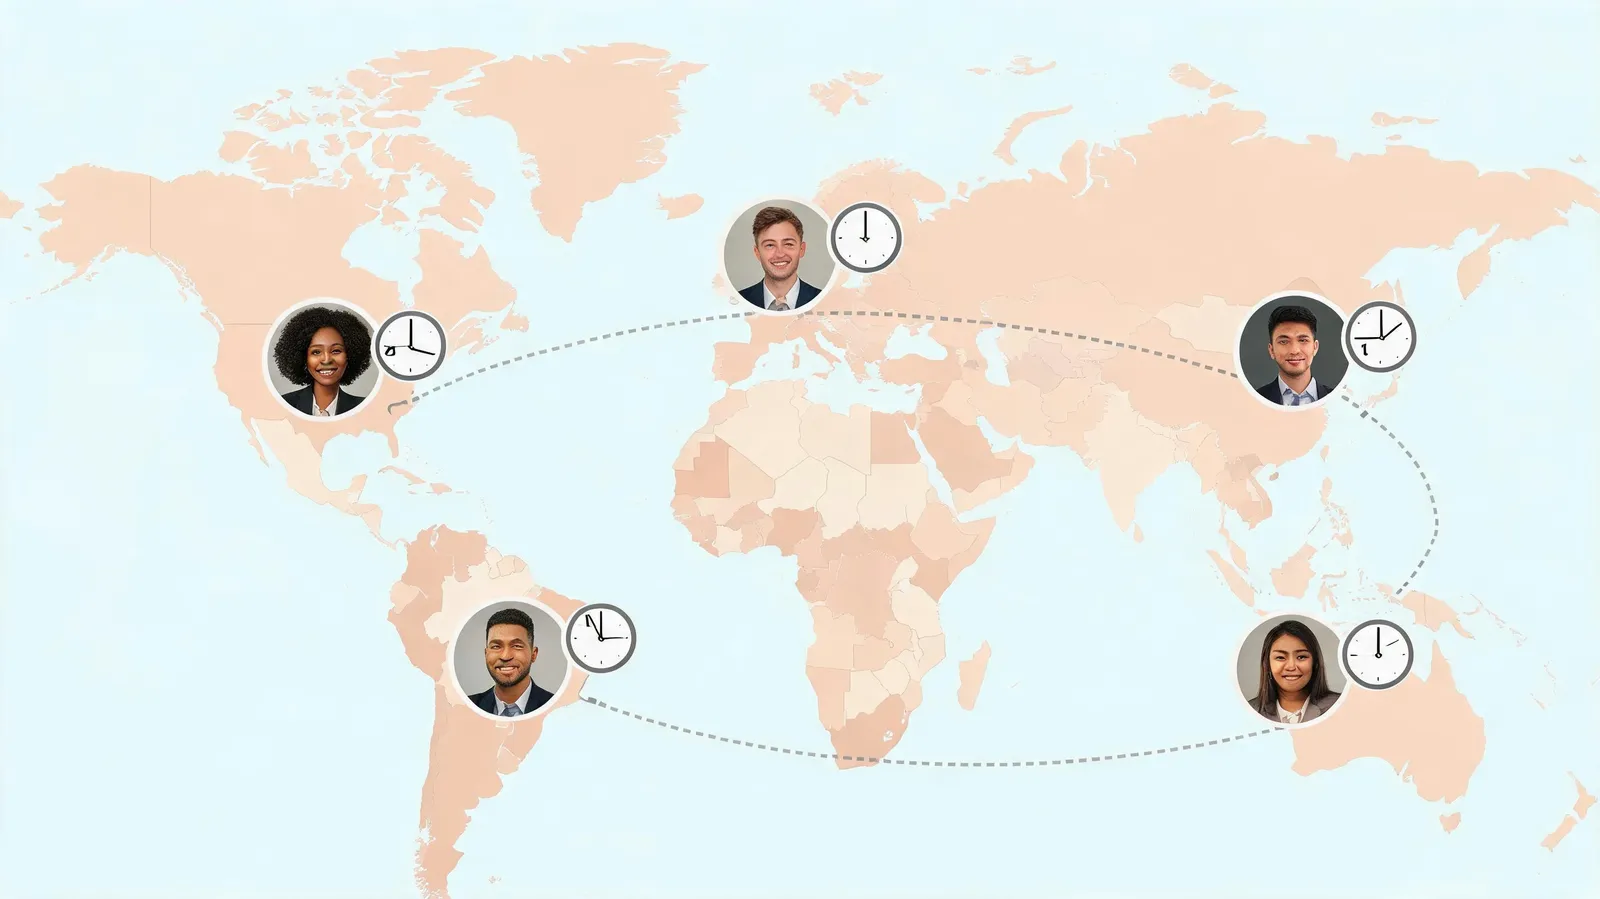
For globally distributed teams, asynchronous collaboration is a necessity rather than merely a convenience. Tools must facilitate non-real-time collaboration through smart notifications, digest emails, and activity feeds that keep everyone informed without overwhelming them. Survey data from US-based remote teams shows that excessive notifications are a leading complaint, contributing to meeting overload and context switching. Tools with smart notification batching—such as GitHub's notification settings and GitLab's notification levels—enable users to customize what they receive and when. Some tools, like Reviewable, provide digest emails that summarize all review activity in a single message, reducing inbox noise.
Video and screen recording integration further strengthens async collaboration. A team spread across 12 time zones used Loom to record short walkthroughs of complex code changes and attached them to pull requests. This cut the need for synchronous meetings by 40% and improved understanding of changes. Vidyard and built-in recording features in some tools offer similar advantages. When evaluating tools, consider how easily reviewers can record and share screen captures, and whether the tool supports inline playback within the review interface.
3. Integration with Version Control and Issue Trackers
Integration with version control systems (GitHub, GitLab, Bitbucket) and issue trackers (Jira, Linear) is fundamental for traceability and for reducing context switching. Native integrations allow code reviews to be linked directly to issues, so that when a pull request is merged, the associated issue is automatically updated. Such traceability is crucial for compliance and for understanding why a change was made. Leading tools like GitHub and GitLab offer deep native integrations with their own platforms and also provide integrations with Jira and Linear. GitHub's Jira integration, for example, lets you transition issues directly from a pull request. GitLab offers similar capabilities with its Jira integration and also supports Linear through its API.
Webhook and API extensibility enable custom workflows. A US-based fintech company built a custom bot using GitHub's API that enforces review policies: if a pull request touches sensitive files, the bot automatically requests reviews from the security team and blocks merge until approved. This level of customization is achievable with tools that offer robust APIs and webhooks. When comparing tools, consider API rate limits, available endpoints, and the ease of building custom integrations. GitHub, GitLab, and Bitbucket provide extensive APIs, while some smaller tools may have limitations.
4. Automation of Review Assignment and Policy Enforcement
Automation reduces manual overhead and enforces standards consistently. Auto-assignment based on code ownership, expertise, or load balancing ensures that the right reviewers are assigned without manual intervention. A case study of a large US enterprise showed that using auto-assignment based on code ownership reduced review assignment time by 80% and improved reviewer satisfaction. Tools like Reviewable, GitHub, and Gerrit use different algorithms: GitHub combines code owners with round-robin, while Gerrit uses a more complex voting system. The choice depends on team structure and priorities.
Policy enforcement through required checks, linter integration, and security scans ensures that code meets quality and security standards before merge. Examples include automated blocking of non-compliant merges when tests fail or when a security scan detects vulnerabilities. An ROI analysis of automated policy enforcement in a US healthcare company found a 50% reduction in security incidents and a 20% faster time-to-market due to fewer manual checks. Tools like GitHub Actions, GitLab CI, and Jenkins can be integrated to run checks automatically. The key is to balance automation with developer productivity—too many checks can slow down the process, while too few can let defects slip through.
Conclusion
Selecting the appropriate code review and collaboration tool requires assessing four key dimensions: inline comment quality, asynchronous collaboration, integration, and automation. For small teams, a tool with simple inline comments and basic automation may be sufficient, while large enterprises may need advanced workflow customization and robust API extensibility. The right tool can improve code quality, accelerate delivery, and increase team satisfaction. Looking ahead, AI-assisted code review and predictive analytics are emerging trends that hold promise for further optimizing review processes. By carefully assessing your team's needs and testing tools against these dimensions, you can choose a solution that enhances collaboration and drives better software outcomes.